

Get Ready to Boost your Prepare for your 100-150 Exam with 90 Questions
Use Free 100-150 Exam Questions that Stimulates Actual EXAM
Cisco 100-150 Exam Syllabus Topics:
| Topic | Details |
|---|---|
| Topic 1 |
|
| Topic 2 |
|
| Topic 3 |
|
NEW QUESTION # 22
You need to connect a computer's network adapter to a switch using a 1000BASE-T cable.
Which connector should you use?
- A. Coax
- B. RJ-11
- C. OS2 LC
- D. RJ-45
Answer: D
Explanation:
1000BASE-T runs over twisted-pair copper and uses the standard RJ-45 connector.
NEW QUESTION # 23
Which component of the AAA service security model provides identity verification?
- A. Auditing
- B. Authentication
- C. Authorization
- D. Accounting
Answer: B
Explanation:
Authentication is the process that verifies a user's or device's identity before granting access.
NEW QUESTION # 24
Which component of the AAA service security model provides identity verification?
- A. Auditing
- B. Authentication
- C. Authorization
- D. Accounting
Answer: B
Explanation:
The AAA service security model consists of three components: Authentication, Authorization, and Accounting.
*Authentication: This is the process of verifying the identity of a user or device. It ensures that only legitimate users can access the network or service.
*Authorization: This determines what an authenticated user is allowed to do or access within the network.
*Auditing/Accounting: This component tracks the actions of the user, including what resources they access and what changes they make.
Thus, the correct answer is C. Authentication.
References :=
*Cisco AAA Overview
*Understanding AAA (Authentication, Authorization, and Accounting)
NEW QUESTION # 25
What is the purpose of assigning an IP address to the management VLAN interface on a Layer 2 switch?
- A. To enable access to the CLI on the switch through Telnet or SSH
- B. To enable the switch to provide DHCP services to other switches in the network
- C. To enable the switch to act as a default gateway for the attached devices
- D. To enable the switch to resolve URLs for the attached the devices
Answer: A
Explanation:
Assigning an IP to the management VLAN interface allows remote access to the switch's CLI via Telnet or SSH for configuration and monitoring.
NEW QUESTION # 26
Which standard contains the specifications for Wi-Fi networks?
- A. LTE
- B. EIA/TIA 568A
- C. IEEE 802.3
- D. IEEE 802.11
- E. GSM
Answer: D
Explanation:
The IEEE 802.11 standard contains the specifications for Wi-Fi networks. It is a set of media access control (MAC) and physical layer (PHY) specifications for implementing wireless local area network (WLAN) computer communication in various frequencies, including but not limited to 2.4 GHz, 5 GHz, and 6 GHz1.
This standard is maintained by the Institute of Electrical and Electronics Engineers (IEEE) and is commonly referred to as Wi-Fi. The standard has evolved over time to include several amendments that improve speed, range, and reliability of wireless networks.
References :=
*The Most Common Wi-Fi Standards and Types, Explained
*802.11 Standards Explained: 802.11ax, 802.11ac, 802.11b/g/n, 802.11a
*Wi-Fi Standards Explained - GeeksforGeeks
NEW QUESTION # 27
Which OSI layer is responsible for end-to-end communication, segmentation, and error recovery between applications running on different hosts?
- A. Presentation
- B. Session
- C. Transport
- D. Network
Answer: C
Explanation:
The Transport layer ensures reliable data transfer through segmentation, flow control, and error recovery, using protocols like TCP and UDP to manage communication between applications.
NEW QUESTION # 28
In the network shown in the following graphic, Switch1 is a Layer 2 switch.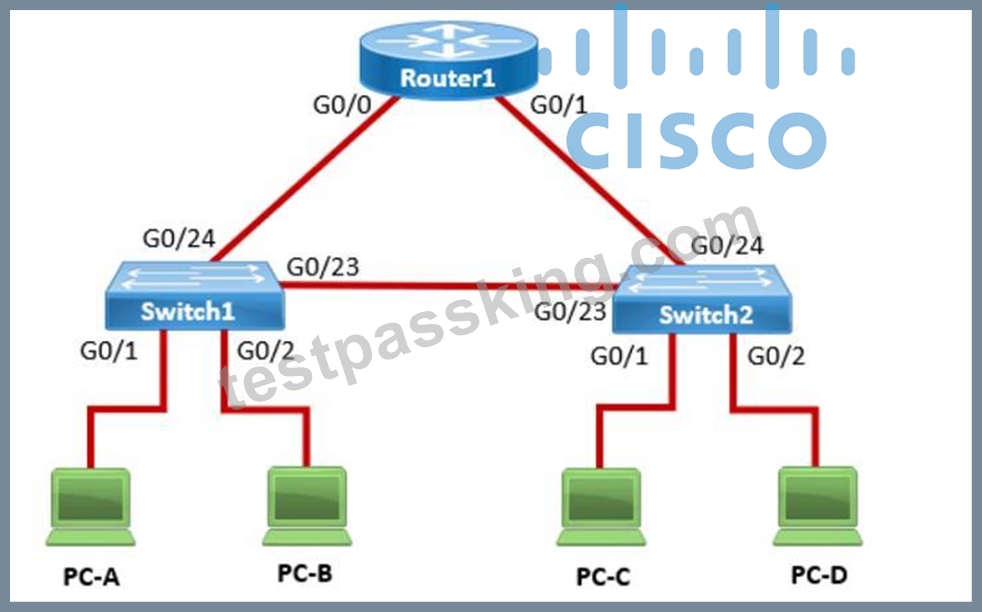
PC-A sends a frame to PC-C. Switch1 does not have a mapping entry for the MAC address of PC-C. Which action does Switch1 take?
- A. Switch1 sends an ARP request to obtain the MAC address of PC-C.
- B. Switch1 drops the frame and sends an error message back to PC-A.
- C. Switch1 floods the frame out all active ports except port G0/1.
- D. Switch1 queries Switch2 for the MAC address of PC-C.
Answer: C
Explanation:
Understanding How Layer 2 Switches Handle Unknown MAC Addresses
Switches operate at Layer 2 (Data Link Layer) of the OSI model and maintain a MAC address table (CAM table) to forward frames efficiently.
* When a switch receives a frame, it checks its MAC address table to see if it knows the destination MAC address.
* If the destination MAC address is not in the table (meaning the switch does not know which port leads to PC-C), the switch follows the flooding behavior.
What Happens When Switch1 Receives a Frame from PC-A to PC-C?
* Switch1 checks its MAC table:
* The source MAC (PC-A) is recorded in the table on port G0/1.
* The destination MAC (PC-C) is not in the table.
* Switch1 does not know where PC-C is:
* It floods the frame out of all active ports except the port it was received on (G0/1).
* This means the frame is sent to:
* Switch2 (via G0/23)
* PC-B (via G0/2)
* Switch2 receives the frame and follows the same process:
* If Switch2 has PC-C's MAC in its table, it forwards the frame appropriately.
* If not, it floods the frame again until PC-C replies.
* Once PC-C responds, Switch1 and Switch2 learn its MAC address and update their tables.
Why Other Options Are Incorrect:
# A. Switch1 queries Switch2 for the MAC address of PC-C.
* Incorrect: Switches do not query other switches directly for MAC addresses. Instead, they rely on learning MAC addresses dynamically through frame forwarding.
# B. Switch1 drops the frame and sends an error message back to PC-A.
* Incorrect: Switches do not drop frames for unknown MAC addresses. Instead, they flood the frames out all ports except the incoming port.
# D. Switch1 sends an ARP request to obtain the MAC address of PC-C.
* Incorrect:
* ARP (Address Resolution Protocol) is only used to resolve IP addresses to MAC addresses.
* Since PC-A is sending a frame (Layer 2), not an IP packet (Layer 3), ARP is not involved here.
Conclusion
Since Switch1 does not know the destination MAC address, it floods the frame out all active ports except the port it was received on. This is the default behavior of Layer 2 switches when they encounter an unknown MAC address.
Thus, the correct answer is:# C. Switch1 floods the frame out all active ports except port G0/1.
References
* Cisco CCNA 200-301 Official Guide - MAC Address Table & Frame Forwarding
* RFC 894 - Standard for Ethernet Frame Forwarding
* Cisco Networking Essentials - Switch Flooding Behavior
NEW QUESTION # 29
Examine the connections shown in the following image. Move the cable types on the right to the appropriate connection description on the left. You may use each cable type more than once or not at all.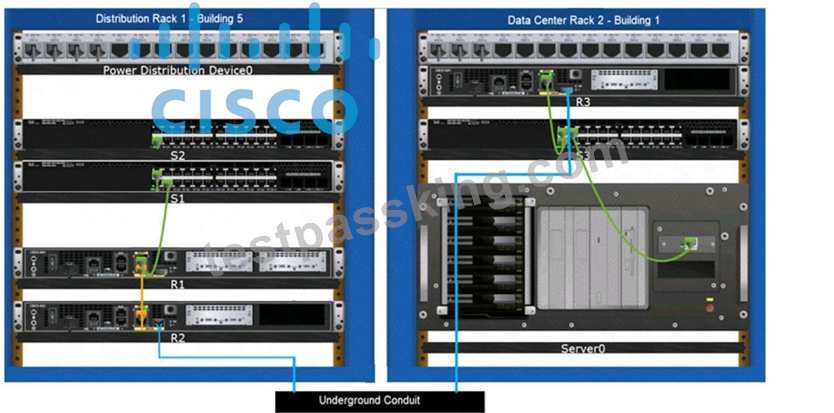
Answer:
Explanation: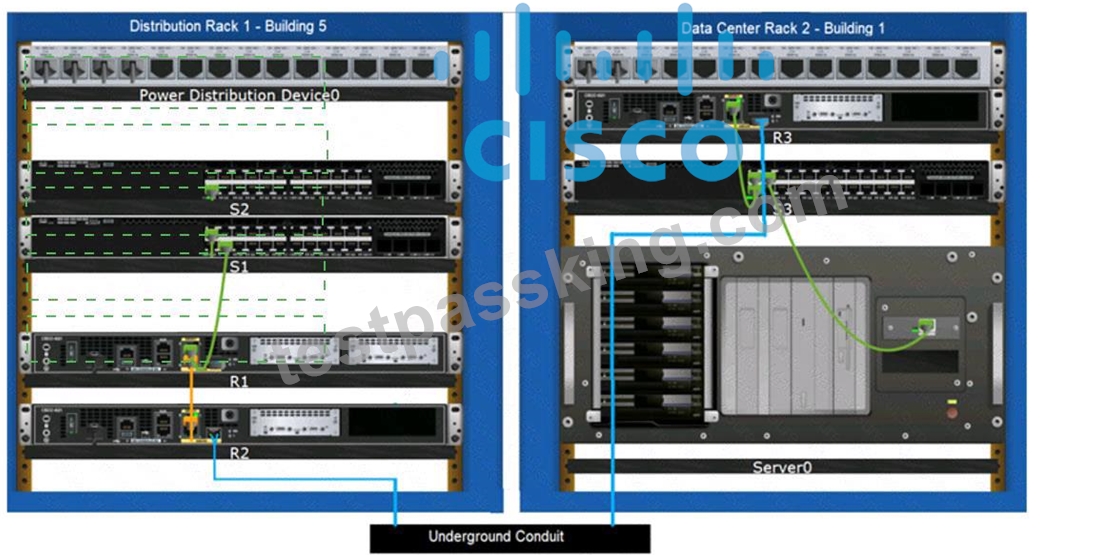
Explanation:
Based on the image description provided, here are the cable types matched with the appropriate connection descriptions:
Connects Switch S1 to Router R1 Gi0/0/1 interface Cable Type: = Straight-through UTP Cable Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduit Cable Type: = Fiber Optic Cable Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1 Cable Type: = Crossover UTP Cable Connects Switch S3 to Server0 network interface card Cable Type: = Straight-through UTP Cable The choices are based on standard networking practices where:
* Straight-through UTP cables are typically used to connect a switch to a router or a network interface card.
* Fiber optic cables are ideal for long-distance, high-speed data transmission, such as connections through an underground conduit.
* Crossover UTP cables are used to connect similar devices, such as router-to-router connections.
These matches are consistent with the color-coded cables in the image: green for switch connections, yellow for router-to-router connections within the same rack, and blue for inter-rack connections. The use of these cables follows the Ethernet cabling standards.
* Connects Switch S1 to Router R1 Gi0/0/1 interface:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect different types of devices, such as a switch to a router.
* Connects Router R2 Gi0/0/0 to Router R3 Gi0/0/0 via underground conduit:
* Cable Type: Fiber Optic Cable
* Explanation: Fiber optic cables are used for long-distance connections, such as those through an underground conduit between buildings.
* Connects Router R1 Gi0/0/0 to Router R2 Gi0/0/1:
* Cable Type: Crossover UTP Cable
* Explanation: A crossover UTP cable is typically used to connect similar devices directly, such as router to router connections.
* Connects Switch S3 to Server0 network interface card:
* Cable Type: Straight-through UTP Cable
* Explanation: A straight-through UTP cable is typically used to connect a switch to an end device, such as a server.
* Straight-through UTP Cable: Used to connect different devices (e.g., switch to router, switch to server).
* Crossover UTP Cable: Used to connect similar devices directly (e.g., router to router, switch to switch).
* Fiber Optic Cable: Used for long-distance and high-speed connections, often between buildings or data centers.
References:
* Network Cable Types and Uses: Cisco Network Cables
* Understanding Ethernet Cabling: Ethernet Cable Guide
NEW QUESTION # 30
Drag and Drop Question
Move each cloud service model on the left to its correct description on the right.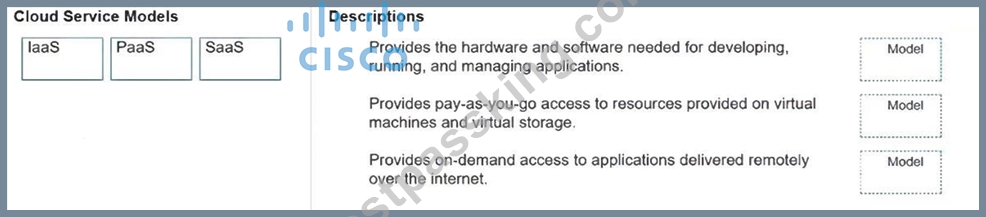
Answer:
Explanation: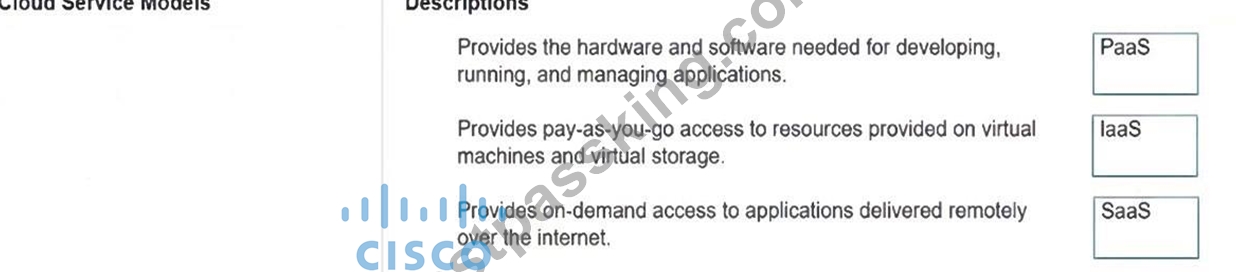
Explanation:
Platform as a Service provides the environment and tools needed to develop, run, and manage applications. Infrastructure as a Service provides virtualized computing resources such as virtual machines and storage on a pay-as-you-go basis. Software as a Service provides ready-to-use applications that users access remotely over the internet.
NEW QUESTION # 31
A host is given the IP address 172.16.100.25 and the subnet mask 255.255.252.0.
What is the CIDR notation for this address?
- A. 172.16.100.25 /21
- B. 172.16.100.25 /22
- C. 172.16.100.25 /23
- D. 172.16.100.25 /20
Answer: B
Explanation:
The CIDR (Classless Inter-Domain Routing) notation for the subnet mask 255.255.252.0 is /22. This notation indicates that the first 22 bits of the IP address are used for network identification, and the remaining bits are used for host addresses within the network1.
References :=
*Subnet Cheat Sheet - 24 Subnet Mask, 30, 26, 27, 29, and other IP Address CIDR Network References
*Subnet Mask to CIDR Notation: The given subnet mask is 255.255.252.0. To convert this to CIDR notation:
*Convert the subnet mask to binary: 11111111.11111111.11111100.00000000
*Count the number of consecutive 1s in the binary form: There are 22 ones.
*Therefore, the CIDR notation is /22.
References:
*Understanding Subnetting and CIDR: Cisco CIDR Guide
NEW QUESTION # 32
Which protocol allows you to securely upload files to another computer on the internet?
- A. SFTP
- B. HTTP
- C. NTP
- D. ICMP
Answer: A
Explanation:
SFTP, or Secure File Transfer Protocol, is a protocol that allows for secure file transfer capabilities between networked hosts. It is a secure extension of the File Transfer Protocol (FTP). SFTP encrypts both commands and data, preventing passwords and sensitive information from being transmitted openly over the network. It is typically used for secure file transfers over the internet and is built on the Secure Shell (SSH) protocol1.
Reference: =
* What Is SFTP? (Secure File Transfer Protocol)
* How to Use SFTP to Safely Transfer Files: A Step-by-Step Guide
* Secure File Transfers: Best Practices, Protocols And Tools
The Secure File Transfer Protocol (SFTP) is a secure version of the File Transfer Protocol (FTP) that uses SSH (Secure Shell) to encrypt all commands and data. This ensures that sensitive information, such as usernames, passwords, and files being transferred, are securely transmitted over the network.
* ICMP (Internet Control Message Protocol) is used for network diagnostics and is not designed for file transfer.
* NTP (Network Time Protocol) is used to synchronize clocks between computer systems and is not related to file transfer.
* HTTP (HyperText Transfer Protocol) is used for transmitting web pages over the internet and does not inherently provide secure file transfer capabilities.
Thus, the correct protocol that allows secure uploading of files to another computer on the internet is SFTP.
Reference: =
* Cisco Learning Network
* SFTP Overview (Cisco)
NEW QUESTION # 33
You want to store files that will be accessible by every user on your network.
Which endpoint device do you need?
- A. Switch
- B. Server
- C. Access point
- D. Hub
Answer: B
Explanation:
A server is the endpoint device designed to host and share files across the network for all users.
NEW QUESTION # 34
Evaluate the graphic.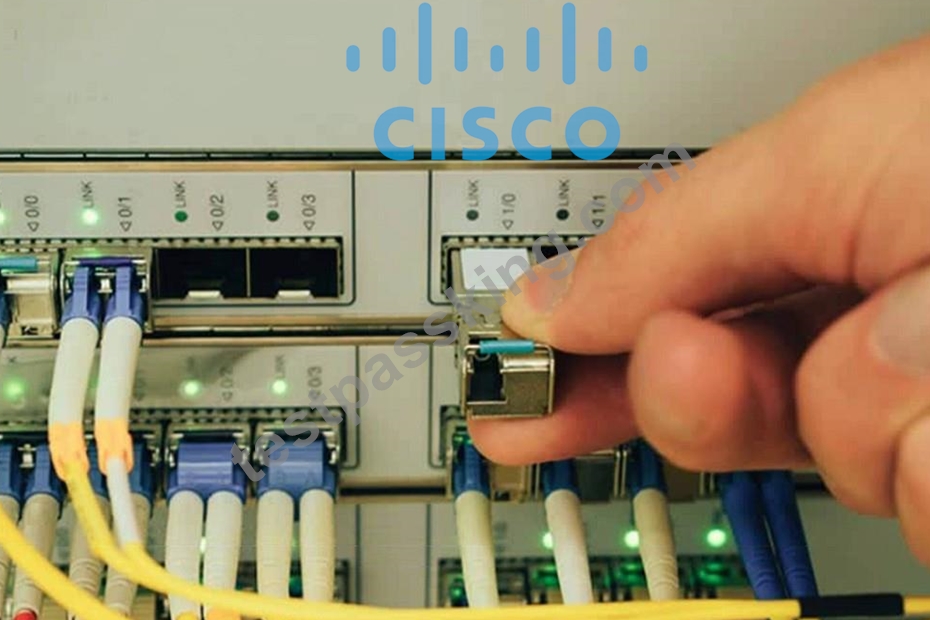
What type of interface is the administrator installing in the router?
- A. PoE
- B. USB
- C. Serial
- D. SFP
Answer: D
Explanation:
The administrator is inserting a small pluggable transceiver used for network connectivity, which is an SFP module. It provides an interface for connecting fiber or copper network links to the router.
NEW QUESTION # 35
A host is given the IP address 172.16.100.25 and the subnet mask 255.255.252.0.
What is the CIDR notation for this address?
- A. 172.16.100.25 /21
- B. 172.16.100.25 /22
- C. 172.16.100.25 /23
- D. 172.16.100.25 /20
Answer: B
Explanation:
The mask 255.255.252.0 has 22 contiguous one bits (16 from the first two octets plus 6 from the third), which corresponds to a /22 prefix.
NEW QUESTION # 36
Drag and Drop Question
Move the security options from the list on the left to its characteristic on the right. You may use each security option once, more than once, or not at all.
Note: You will receive partial credit for each correct answer.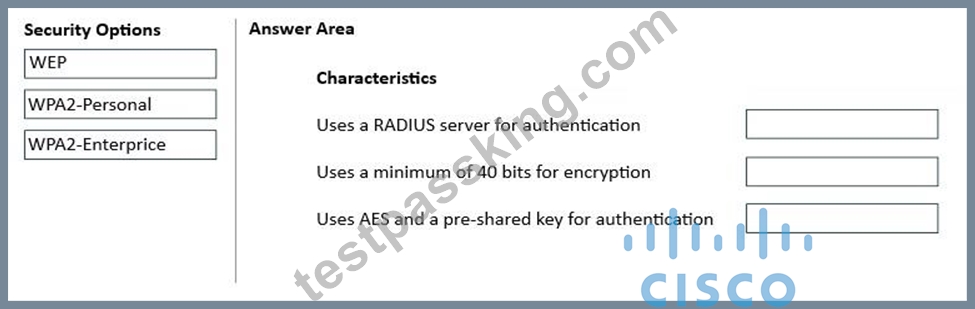
Answer:
Explanation: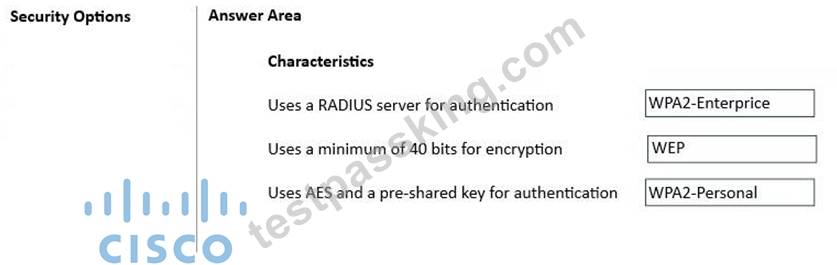
NEW QUESTION # 37
What is the most compressed valid format of the IPv6 address 2001 :0db8:0000:0016:0000:001b: 2000:0056?
- A. 2001:db8: 0:16: :1b: 2000:56
- B. 2001:db8: : 16: : 1b:2:56
- C. 2001:db8: 16: :1b:2:56
- D. 2001:db8: : 16: : 1b: 2000: 56
Answer: A
Explanation:
IPv6 addresses can be compressed by removing leading zeros and replacing consecutive groups of zeros with a double colon (::). Here's how to compress the address 2001:0db8:0000:0016:0000:001b:2000:0056:
* Remove leading zeros from each segment:
* 2001:db8:0000:0016:0000:001b:2000:0056 becomes 2001:db8:0:16:0:1b:2000:56
* Replace the longest sequence of consecutive zeros with a double colon (::). In this case, the two consecutive zeros between the 16 and 1b:
* 2001:db8:0:16::1b:2000:56
Thus, the most compressed valid format of the IPv6 address is 2001:db8:0:16::1b:2000:56.
References :=
* Cisco Learning Network
* IPv6 Addressing (Cisco)
NEW QUESTION # 38
Hotspot Question
For each statement about bandwidth and throughput, select True or False.
Note: You will receive partial credit for each correct selection.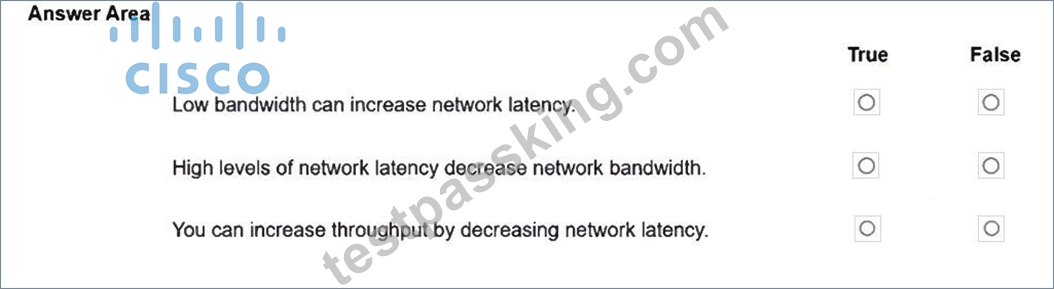
Answer:
Explanation: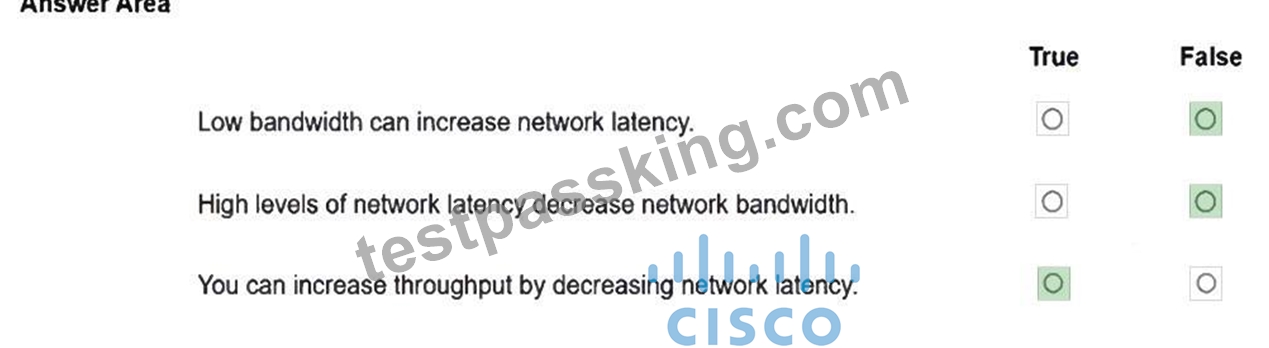
Explanation:
Bandwidth is the network's capacity, while latency is the delay in transmission, so low bandwidth does not by itself increase latency. High latency does not change the actual bandwidth of a link, but it can reduce how efficiently data is delivered. Reducing latency can improve the rate of successful data delivery, which increases throughput.
NEW QUESTION # 39
Which type of cable is commonly used for Ethernet connections and contains twisted pairs to reduce electromagnetic interference?
- A. Fiber optic
- B. Coaxial
- C. Serial
- D. Twisted pair
Answer: D
Explanation:
Twisted pair cables reduce interference by twisting wires together, improving signal integrity and making them the most widely used medium for Ethernet LAN connections.
NEW QUESTION # 40
Which address is a link-local IPv6 address?
- A. fe80::261:2eff:fe10:7561
- B. fdf8:f535:82e4::53
- C. ff01:0:0:0:0:0:0:2
- D. 2001:db8:85a3:8d3:1319:8a2e:370:7348
Answer: A
Explanation:
Link-local IPv6 addresses use the prefix fe80::/10 and are automatically used for communication on the local link. The address shown begins with fe80, so it is a link-local address.
NEW QUESTION # 41
What is the CIDR prefix notation for a subnet mask of 255.255.0.0?
- A. /16
- B. /32
- C. /8
- D. /24
Answer: A
Explanation:
The subnet mask 255.255.0.0 has 16 consecutive 1 bits in the network portion, so its CIDR prefix length is /16.
NEW QUESTION # 42
A local company requires two networks in two new buildings. The addresses used in these networks must be in the private network range.
Which two address ranges should the company use? (Choose two.)
Note: You will receive partial credit for each correct selection.
- A. 192.16.0.0 to 192.16.255.255
- B. 192.168.0.0 to 192.168.255.255
- C. 172.16.0.0 to 172.31.255.255
- D. 11.0.0.0 to 11.255.255.255
Answer: B,C
Explanation:
192.168.0.0-192.168.255.255 is the 192.168.0.0/16 private address block.
172.16.0.0-172.31.255.255 is the 172.16.0.0/12 private address block.
NEW QUESTION # 43
Drag and Drop Question
Move each protocol or device type from the list on the left to the correct OSI layer on the right.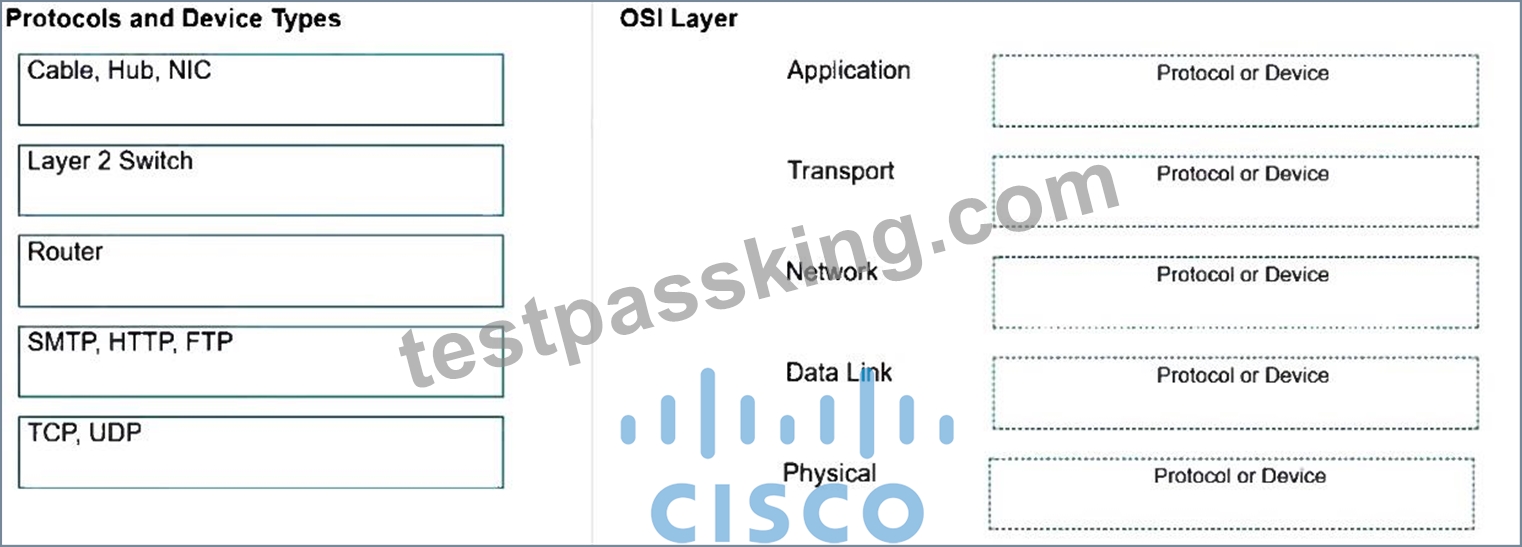
Answer:
Explanation: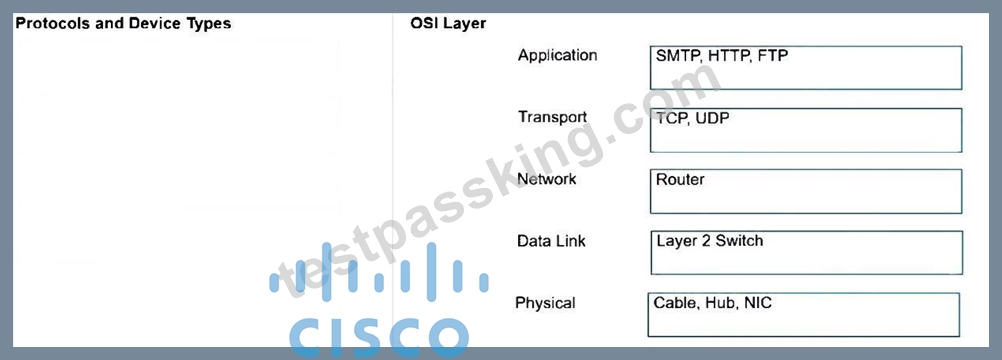
Explanation:
SMTP, HTTP, and FTP are application layer protocols used by end-user network services. TCP and UDP operate at the transport layer and manage end-to-end delivery between applications. A router makes forwarding decisions using Layer 3 addressing, so it belongs to the network layer. A Layer 2 switch forwards frames using MAC addresses, so it belongs to the data link layer.
Cables, hubs, and network interface hardware are associated with the physical transmission of signals.
NEW QUESTION # 44
Hotspot Question
For each statement about the output, select True or False.
Note: You will receive partial credit for each correct selection.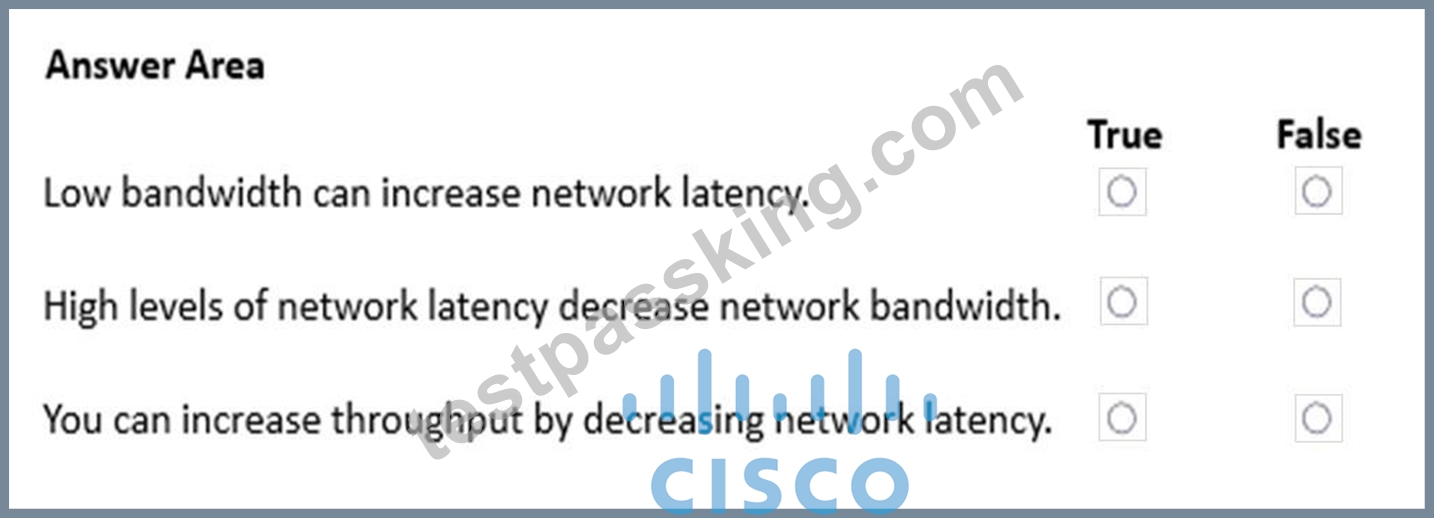
Answer:
Explanation: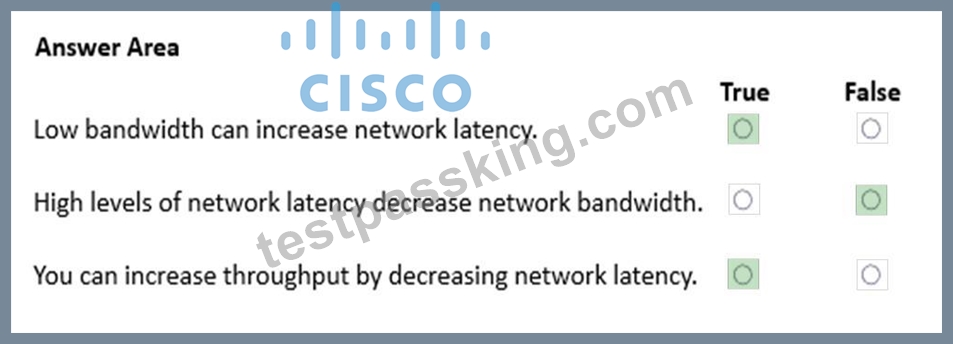
NEW QUESTION # 45
......
BEST Verified Cisco 100-150 Exam Questions (2026) : https://www.testpassking.com/100-150-exam-testking-pass.html
Get 100% Real 100-150 Free Online Practice Test: https://drive.google.com/open?id=1mlEhi0r8VC8tI7nohknsz0jyOUQtz-0c