

[Mar-2024] Download Real SC-400 Exam Dumps for candidates. 100% Free Dump Files
Prepare Important Exam with SC-400 Exam Dumps(2024)
To take the SC-400 exam, candidates must have a solid understanding of Microsoft 365 services, including Azure Information Protection, Microsoft Cloud App Security, and Microsoft Defender for Endpoint. They should also have experience with Microsoft Identity and Access Management solutions, such as Azure Active Directory and Microsoft Intune.
Prerequisites of Microsoft SC-400 Exam
Microsoft Information Protection Administrator Certification is designed to verify an individual's knowledge of identity, security, and compliance. To become a Microsoft Information Protection Administrator, you must pass three exams. As a Microsoft Information Protection Administrator, you protect your organization from the growing risks of information protection failures by helping to manage and implement data-protection strategies. You can also build on your expertise with the Microsoft Office 365 service and improve your overall IT skills as you advance in your career. Despite this certification being called “Microsoft Information Protection Administrator”, there are several additional certifications that are required to be obtained before you can be eligible to take the test. For example, the SC-900 - Microsoft Security, Compliance, and Identity Principles certification is highly recommended. This certification covers the fundamentals of security, compliance, and identity. The second exam that is required is the SC-400 - Microsoft Information Protection Administrator Certification. This certification helps to specialize on compliance. The third exam is the MCP: Microsoft Certified Professional (MCP) which will help you validate your understanding of core IT topics including networking and cloud computing concepts.
NEW QUESTION # 88
You have the files shown in the following table.
You configure a retention policy as shown in the exhibit.
The start of the retention period is based on when items are created. The current date is January 01, 2021.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-policies-sharepoint?view=o365-worldwide
NEW QUESTION # 89
You have a Microsoft 365 E5 subscription that uses Microsoft Teams and contains a user named User1.
You configure Microsoft Purview Information Barriers.
You need to identify which information barrier policies apply to User1.
Which cmdlet should you use?
- A. Get-InformationBarrierPoliciesApplicationStatus
- B. Get-InformtionBarrierPolicy
- C. Get-InformtionBarrierRecipientStatus
- D. Get-OrganizationSegaent
Answer: C
NEW QUESTION # 90
You need to recommend a solution that meets the compliance requirements for viewing DLP tooltip justifications.
What should you recommend?
- A. Instruct the compliance department users to review the False positive and override report.
- B. Instruct the compliance department users to review the DLP incidents report.
- C. Configure an Azure logic app to route DLP notification emails to the compliance department.
- D. Configure a Microsoft Power Automate workflow to route DLP notification emails to the compliance department.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/view-the-dlp-reports?view=o365-worldwide
Topic 2, Contoso Case Study
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Microsoft 365 Environment
Contoso has a Microsoft 365 FS tenant I he tenant contains the administrative user accounts shown in the following table.
Users store data In the following locations:
* SharePoint sites
* OneDrive accounts
* Exchange email
* Exchange public folders
* Teams chats
* Teams channel messages
When users in the research department create documents, they must add a 10-dig>t project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1. Site2. Site3. and Site4.
Site2 contains the files shown in the following table.
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Sile3 stores documents related to the company's projects. The documents are organized In a folder hierarchy based on the project.
Slte4 has the following two retention policies applied:
* Name: SitetKetentionPolicy1
* Locations to apply the policy: Site4
* Delete items older than:2 years
* Delete content based on: When items were created
* Name: Site4RetentionPolicy2
* Locations to apply the policy. Sile4
* Retain items for a specific period: 4 years
* Start the retention period based on: When items were created
* At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research departments were leaked.
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
* Name: DLPpolicy1
* Locations to apply the policy; Site2
* Conditions:
* Content contains any of these sensitive info types: SWIF F Code
* Instance count: 2 to any
* Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
* All administrative users must be able to review DLP reports.
* Whenever possible, the principle of least privilege must be used.
* For all users, all Microsoft 365 data must be retained for at least one year.
* Confidential documents must be detected and protected by using Microsoft 365.
* Site1 documents that include credit card numbers must be labeled automatically.
* All administrative users must be able to create Microsoft 365 sensitivity labels.
* After a project is complete, the documents in Site3 that relate to the project must be retained for 10 years
NEW QUESTION # 91
You plan to implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You need to identify which end user activities can be audited on the endpoints, and which activities can be restricted on the endpoints.
What should you identify for each activity? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/endpoint-dlp-learn-about?view=o365-worldwide
NEW QUESTION # 92
You have a Microsoft 365 E5 tenant that contains the policies shown in the following table.
A file named File1 has all the policies applied.
How long will File1 be retained?
- A. File1 will be deleted automatically after seven years.
- B. File1 will be retained until the file is deleted manually.
- C. File1 will be deleted automatically after five years.
- D. File1 will be deleted automatically after 10 years.
Answer: D
NEW QUESTION # 93
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.
You have a retention policy that has the following configurations:
Name: Policy1
Retain items for a specific period: 5 years
Locations to apply the policy: Exchange email, SharePoint sites
You place a Preservation Lock on Policy1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation: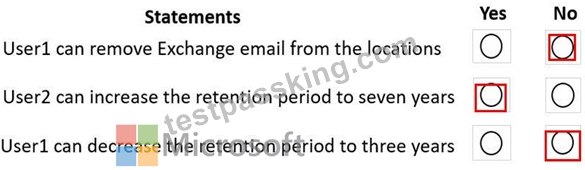
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-preservation-lock?view=o365-worldwide
NEW QUESTION # 94
You have a Microsoft 365 E5 subscription.
You have the alerts shown in the following exhibit
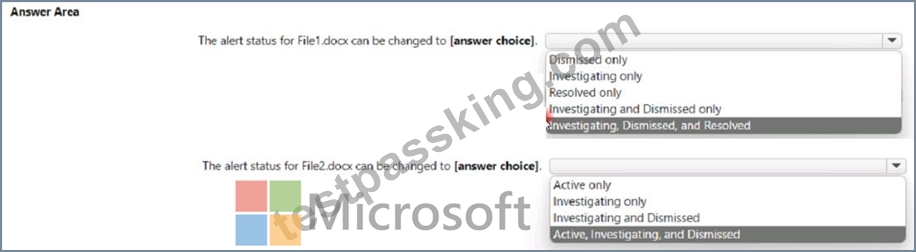
Answer:
Explanation:
NEW QUESTION # 95
You have a Microsoft 365 E5 tenant that contains the users shown in the following table.
You have a retention policy that has the following configurations:
Name: Policy1
Retain items for a specific period: 5 years
Locations to apply the policy: Exchange email, SharePoint sites
You place a Preservation Lock on Policy1.
For each of the following statements, select Yes if the statement is true. Otherwise, select No.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/retention-preservation-lock?view=o365-worldwide
NEW QUESTION # 96
You have a Microsoft 365 tenant that uses trainable classifiers.
You are creating a custom trainable classifier.
You collect 300 sample file types from various geographical locations to use as seed content. Some of the file samples are encrypted.
You organize the files into categories as shown in the following table.
Which file categories can be used as seed content?
- A. Category1 and Category3 only
- B. Category4 and Category6 only
- C. Category4 and Category5 only
- D. Category2. Category3. and Category5 only
Answer: B
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/classifier-get-started-with?view=o365-worldwide
https://docs.microsoft.com/en-us/sharepoint/technical-reference/default-crawled-file-name-extensions-andparsed
NEW QUESTION # 97
You need to meet the technical requirements for the confidential documents.
What should you created first, and what should you use for the detection method? To answer, select the appropriate options in the answer area.
NOTE: Each correct selection is worth one point.
Answer:
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/create-a-custom-sensitive-information-type?view=o365-worldwide
NEW QUESTION # 98
You have a Microsoft 365 tenant.
You create the following:
A sensitivity label
An auto-labeling policy
You need to ensure that the sensitivity label is applied to all the data discovered by the auto-labeling policy.
What should you do first?
- A. Create a trainable classifier.
- B. Run the Enable-TransportRule cmdlet.
- C. Run the policy in simulation mode.
- D. Enable insider risk management.
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/apply-sensitivity-label-automatically?view=o365-worldwide
NEW QUESTION # 99
You are implementing Microsoft Office 365 Message Encryption (OME) for a Microsoft 365 tenant named contoso.com.
You need to meet the following requirements:
* All email to a domain named fabhkam.com must be encrypted automatically.
* Encrypted emails must expire seven days after they are sent-
What should you configure for each requirement? To answer, select the appropriate options NOTE: Each correct selection is worth one point.
Answer:
Explanation:
NEW QUESTION # 100
After you answer a question in this section, you will NOT be able to return to it. As a result, these questions will not appear in the review screen.
You implement Microsoft 365 Endpoint data loss prevention (Endpoint DLP).
You have computers that run Windows 10 and have Microsoft 365 Apps installed. The computers are joined to Azure Active Directory (Azure AD).
You need to ensure that Endpoint DLP policies can protect content on the computers.
Solution: You onboard the computers to Microsoft Defender for Endpoint.
Does this meet the goal?
- A. Yes
- B. No
Answer: A
NEW QUESTION # 101
You have a Microsoft OneDrive for Business folder that contains the files shown in the following table.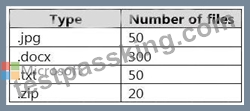
In Microsoft Cloud App Security, you create a file policy to automatically apply a classification.
What is the effect of applying the policy?
- A. The policy will apply to all the files. The policy will classify only 100 files daily.
- B. The policy will apply to only the .docx and .txt files. The policy will classify the files within 24 hours.
- C. The policy will apply to only the .docx files. The policy will classify only 100 files daily.
- D. The policy will apply to only the .docx and .txt files. The policy will classify the files immediately.
Answer: C
Explanation:
Reference:
https://docs.microsoft.com/en-us/cloud-app-security/azip-integration
NEW QUESTION # 102
You need to recommend a solution that meets the compliance requirements for Dropbox.
What should you recommend?
- A. Edit an existing retention label that enforces the item deletion settings.
- B. Create a DLP policy that applies to devices.
- C. Create a retention label that enforces the item deletion settings.
- D. Create a DLP policy that applies to Cloud App Security.
Answer: D
Explanation:
Reference:
https://docs.microsoft.com/en-us/microsoft-365/compliance/dlp-use-policies-non-microsoft-cloud-apps?
view=o365-worldwide
Topic 2, Contoso Case Study
Overview
Contoso, Ltd. is a consulting company that has a main office in Montreal and three branch offices in Seattle, Boston, and Johannesburg.
Microsoft 365 Environment
Contoso has a Microsoft 365 FS tenant I he tenant contains the administrative user accounts shown in the following table.
Users store data In the following locations:
* SharePoint sites
* OneDrive accounts
* Exchange email
* Exchange public folders
* Teams chats
* Teams channel messages
When users in the research department create documents, they must add a 10-dig>t project code to each document. Project codes that start with the digits 999 are confidential.
SharePoint Online Environment
Contoso has four Microsoft SharePoint Online sites named Site1. Site2. Site3. and Site4.
Site2 contains the files shown in the following table.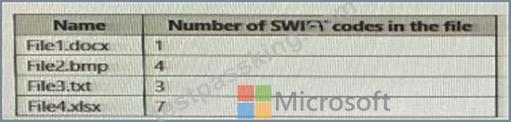
Two users named User1 and User2 are assigned roles for Site2 as shown in the following table.
Sile3 stores documents related to the company's projects. The documents are organized In a folder hierarchy based on the project.
Slte4 has the following two retention policies applied:
* Name: SitetKetentionPolicy1
* Locations to apply the policy: Site4
* Delete items older than:2 years
* Delete content based on: When items were created
* Name: Site4RetentionPolicy2
* Locations to apply the policy. Sile4
* Retain items for a specific period: 4 years
* Start the retention period based on: When items were created
* At the end of the retention period: Do nothing
Problem Statements
Management at Contoso is concerned about data leaks. On several occasions, confidential research departments were leaked.
Planned Changes
Contoso plans to create the following data loss prevention (DLP) policy:
* Name: DLPpolicy1
* Locations to apply the policy; Site2
* Conditions:
* Content contains any of these sensitive info types: SWIF F Code
* Instance count: 2 to any
* Actions: Restrict access to the content
Technical Requirements
Contoso must meet the following technical requirements:
* All administrative users must be able to review DLP reports.
* Whenever possible, the principle of least privilege must be used.
* For all users, all Microsoft 365 data must be retained for at least one year.
* Confidential documents must be detected and protected by using Microsoft 365.
* Site1 documents that include credit card numbers must be labeled automatically.
* All administrative users must be able to create Microsoft 365 sensitivity labels.
* After a project is complete, the documents in Site3 that relate to the project must be retained for 10 years
NEW QUESTION # 103
In Microsoft Exchange Online, you have a retention policy named Policy1 that applies a retention tag named Tag1.
You plan to remove Tag1 from Policy1.
What will occur when you remove the tag from Policy1?
- A. The content will remain tagged and the Managed Folder Assistant will process Tag1.
- B. Tag1 will be removed if Policy1 applied the tag to the content.
- C. The content will remain tagged, but the Managed Folder Assistant will ignore Tag1.
Answer: A
Explanation:
Reference:
https://docs.microsoft.com/en-us/exchange/security-and-compliance/messaging-records-management/ retention-tags-and-policies#removing-or-deleting-a-retention-tag-from-a-retention-policy
NEW QUESTION # 104
......
SC-400 Questions - Truly Beneficial For Your Microsoft Exam: https://www.testpassking.com/SC-400-exam-testking-pass.html
Pass Exam Questions Efficiently With SC-400 Questions: https://drive.google.com/open?id=1KPW_p8-0TEqP5kXoOWzHXGFj3zaS9gMf